Sunday, 8 January 2017

弹指一挥间

二十五载, 弹指一挥间。

在我上大学前, 父亲就向我们兄弟姐妹灌输:今后要自力更生。一开始没有注意还有“弦外之音”,因为那时国家也号召“自力更生,丰衣足食”。渐渐便体会到父亲在暗示我们:家底就是这样啦, 你们今后就自食其力吧!

我二十六岁那年,父亲查出癌症后两个月就没了。这么些年来,自己真的是自力更生一步一个脚印走过来。有苦有乐。我想,父亲对我的这个教育是成功的。如今到了我给我的子女灌输这个思想了,难道这与生命一样轮回?一代一代,周而复始?愿现今这个社会依然能给儿辈们一个自食其力的环境!

父亲去世时年仅五十七岁。现在我自己也年过半百,两鬓已显斑白。一个多月前一位大学同学离世让我再次感到生命的无奈。然我心依然年轻,因为我还没有去想如何养老自己,依然认为自己能活到老,学到老,干到老。

愿自己能一直自力下去,直到生命的终结。

奢愿乎?人各有天命,且行且珍惜吧。

爸爸,儿依然想你。期待下一次与你梦中相会。

片言只语,谨以此纪念离开我们已经二十五年的父亲。

Thursday, 18 August 2016

Results day

今天是 A Level 发榜日 (2016/08/18, http://www.bbc.co.uk/news/education-37107004)。我高兴,因为儿子全部科目得A*, 因而可以入剑桥就读。


我第一时间跪拜东方,感谢上苍,同时希望能告知疼他的外婆,还有他没能见到的外公和爷爷。愿他们泉下有知,也能为之高兴。

Saturday, 10 October 2015

悼岳母大人

下午五点半回家,才获噩耗,与妻抱头恸哭。

知道这一次不会有奇迹,所以妻最大的愿望是陪妈妈走完人生的最后一程。昨日周五从机场接她回家的路上,我还说,要不你下周一就再去办签证... 未曾想, 妈妈今天就走了...

也许妈妈走的时候已经放下一切。可最后一刻,妻不在她身边,她是否有些遗憾?对妻而言, 这将是她未来一生之痛。我也会为此内疚后半辈子。因为妻回来之前征求我的意见,我没有建议她留下来。

岳母是一个典型的湖南人,意志坚强。去年全家回疆探亲,离开的时候,却见岳母哭了,她说不知是否还能再见到你们?我抱了抱她老人家,安慰她说,等她中风恢复好些,再来英国住住。未曾想,从此一别,竟成永诀...

这次回来,妻带回一本相册。那是岳母精心整理的妻成长的过程。我想平时她老人家见不到幺闺女的时候,就会拿出来看看,以解相思之苦。如今斯人已去,阴阳两隔。见妻痴痴的望着岳母遗照,我竟忍不住泪流满面...

我想,人无论多大年纪,只要有父母健在,心就有寄托。如今,妻失去了双亲,内心有多悲哀...

2015年10月10号,北京时间18点40分,岳母走了,纽带断了...

愿岳母大人安息...

Sunday, 10 May 2015

Angiogram Procedure 心脏造影

二月份以来,身体一直感觉不适。乏力,气短(缺氧似的),左胸口有轻微疼痛,一开始没有在意,因为我用左手打羽毛球。

三月九号,是一个繁忙的星期一。当晚我严重不适。第二天上午看GP, 期间我提及多年前的往事。三十多岁时在国内做体检,医生说我的心电图比我的实际年龄老10岁(至今不知何意,但肯定不是好事)。HEART ATTACK 有生命危险,GP不敢怠慢,安排验血,ECG(心电图)。GP看完心电图,认为不是心脏的问题,但还是给我开了AMLODIPINE, GTN SPRAYER。同时安排我两周后去CHEST PAIN CLINIC 进一步检查。

服了一周的AMLODIPINE,未见好转,副作用还挺大,遂停服。三月23号,在CLINIC 又做了平静状态下的ECG,没有问题。接着做了跑步机上的ECG, 结果有些“不稳定”。专家组认为没有问题,但为了得出一个明确的结论,建议我做 ANGIOGRAM(冠状动脉造影),  并嘱咐我继续服药,提醒我如果喷了GTN 10-20 分钟后症状未见好转就CALL 999。

ANGIOGRAM 安排在5月1号。可是4月18号凌晨4点又感严重不适。心跳从70跃到90。遂叫急救,送医院。又是验血,ECG。值班医生仍然认为不是心脏问题。因为是周末,没有专家,遂安排我留院。期间,遇到一个患者,类似病症,医生认为也不是心脏问题。我听他跟医生谈话,知道他是累的,我估计自己也是累的。不过他是体力,我是脑力。

周一专家来,认为我没有心脏问题,打发我出院(我巴不得,医院里根本睡不好),并打赌(他开玩笑说他喜欢打赌)说5月1号的检查也不会有问题。

既然安排了,就做吧。5月1号,我自己开车去了Wycombe Hospital(老婆随行,她负责接我出院。按规定,手术后我自己是不能开车的)。医院离我家1个小时的路程,因上班高峰, 走了一个半小时,早晨9点半到达医院停车场。

我的预约时间是10点,还有半个小时,所以不紧不慢走入大厅,向前台问清Cardiac Day Unit 怎么走。

Cardiac Day Unit有一个自己的前台,我在那里报到。看到白板上有我的名字,时间。

护士安排了一个床位,给了我一件长袍,还有一条薄型纱织状半透明裤头,叫我换上。
完成后,她就过来给我量体重,体温,血压,还做了一次ECG。随后就是Paperwork,问我有什么病史,对什么过敏等。

然后就是等待。期间我注意到边上还有两位病人,年纪约65岁左右,比我先到。我猜想自己排在他们后面,第三位。

半天没有动静。后来有个护士过来跟我们仨道歉,说有个poor man,要先做。我们的肯定延迟了。

再后来一个自称Consultant的医生走来,问我是否知道今天要做的手术是什么。我回答说知道,就是用一个细金属线通过股动脉通达心脏。他纠正说,正常情况下通过腕部动脉,除非有任何原因通过腕部动脉不能通达前心区才再试股动脉。他随后说这种手术途中有可能出现并发症,如心机梗塞,肾衰竭等。我笑答,这听起来很恐怖。他解释说,这种几率只有千分之一,权衡利弊,建议我做了,同意的话就在表格上签个字吧,或者把表格留下,让我看看,签字后交护士也可。

我让他将表格留下。但没有去细读,回头问老婆意见。老婆说你都来了,难道要无果而返吗?医生的并发症声明,还有之前在中文网看到的关于心脏造影的信息,让我有所恐惧。加上两周前的折腾,我已经认同专家的打赌-我不应有心肌缺血性心脏病。这个手术值得做吗?老婆的话让我不再犹豫。豁出去了,签!

老婆陪我又坐了一会儿。我心想她在边上,也做不了什么,就让她离开了,去附近的shopping mall 逛逛,约好做完后给她发短信。

包里带了两本女儿的书(Horrible Maths and Horrible Nature。专业书看烦了,一时间又找不到自己感兴趣的闲书)。随手拿出一本打发时间。

将近11点了,还没有动静。遂拿出手机,看看有无WI-FI。 都要密码,又将其扔回包里,不得已拿出第二本书消遣。

11点后(没看具体时间),第一位患者终于被叫走。后来轮到第二位,我注意到第二位回来时时间已经12点半多了。我估计自己应该是午饭后了。

继续等待。期间对面的患者用手机向家里汇报,我观察他术前术后好像没有什么变化,自己就宽心多了。只是担心我这样一个小体格,细胳膊,腕部动脉够不够粗?行不行(前两个患者,一个1米7,另一个至少1米8)?

下午1点20, 护士过来通知说该我了。并领我徒步走到对面30米开外的  LAB, LAB边上就是一个Theatre(真正的手术室),我估计出现异常情况需要做胸外科手术的就可以马上移到隔壁。

引导护士让我在走廊里正对着LAB大门的一个椅子上坐下。他推开大门跟里边确认是否一切就绪。

我屁股还没坐稳,又被叫起,显然里边已经准备停当。我走进LAB,见有医生护士4-5个,大多坐在左手边的控制室。他们刚吃完中午饭,在一起闲聊说笑呢。

很快我就按要求平躺在台上。右手手心向上,平放在一个稍稍外展的支架上。护士给我盖上手术用的被单。随后听到拆包声,大概是准备手术器械。后来才知道这些器械都是一次性的,用后就扔了。一会医生说要给我清洁一下右手腕,有点凉。之后又将我的右手放回原处。我不知道是否有局部麻醉剂,我自己认为没有,因为我活动了下手指,腕部有感觉。

我猜想准备工作完成了,可迟迟不见下一步。后有护士走到我跟前,告诉我主刀医生去吃饭了,一会儿就回来,让我耐心等一会儿。我心想,三个多小时都等过来了,再等几分钟不算什么。但毕竟躺在手术台上,那是脑子里思绪急速翻腾。不过我还是利用这个机会祷告了一下。

一会儿,我听到洗手声,估计主刀医生来了。他走到我跟前,我们相互道了声下午好,他就开始跟我聊天,问我什么时候心脏区域觉得不舒服。随即我右腕感觉有一下刺痛,知道针头已经扎入腕动脉。医生继续跟我聊,我边回答,边听到嗖嗖的声音,我猜想那是主刀医生在送入导线呢(后来想想,这个过程跟我用Drain Rods清理下水道似的)。同时我感到整个右臂发紧,发热。右脸也有些发烫。但没有疼痛感。心脏那里一点感觉也没有。接着,医生开始跟他的同事说话,我听不清,也没有心思去听,注意力完全在我的右臂上。这时,在我胸上方的X光探测仪开始转来转去,大概是在拍各个角度的照片。这个过程持续了2-3分钟,然后又听到嗖嗖的声音,然后手腕觉得更紧了(后来才看到那是TR  band 加压固定)。随后医生对我说,完成了。

从针头扎入,到TR  band 固定,我估计整个过程也就5-6分钟。自己事先被告知大约要15分钟到半个小时,就好奇地问医生为何如此之快,医生回答,你的心脏没有问题,就快点。
随后,护士帮我坐上轮椅,我向全体医生护士道谢。

我被轮椅车推回观察室。看了看墙上的钟,1点41分。稍作安顿,护士问我吃点什么。说实在的,尽管自前晚八点后就按规定没吃东西(水也没喝),但一点没有觉得饿(大概是心情完全专注在这个手术上,注意力分散了)。不过还是要了些三明治,一杯茶。一会儿食物送来了,其中还有一大杯水。护士说还有一大杯,我估计总量大约2升水,要我在2小时内喝完。这水是稀释血液中的造影染料,否则对肾功能会有影响。在这2小时内,每隔15分钟,护士过来量一次血压,检查一下伤口,抽掉一点TR  band中的空气(逐步减压)。

下午3点45分,护士给我清洗了伤口,贴上dressing(就是plasters),调整TR  band松紧度,交代我今后两天内的注意事项,我就被允许出院了。

检查结果当时就出来了- no ischemic heart disease。既然没有物理上的病症,看来比较符合心脏神经官能症,下一步恐怕只能看神经内科了。

现在回想一下,这个手术还是很安全的。事实上,这里根本不称之为手术(operation)。另外,事前我被告知在腕部会有一个切口(incision)。但我觉得 扎孔(puncture)比较达意。

最后,对器械感兴趣的朋友可以看看。

TR Band

手术器械


手术示意图

具体可见

http://www.terumo-europe.com/endovascular/angiography.php

http://vygon.co.uk/products/group/arterial-catheters


电饭锅

家里的美的电饭锅服役四年了。只有一点我不满意的,内锅倒入热水清洗时,会闻到一股电木烧糊的味道。不但涂层锅有,不锈钢锅也有。很是奇怪,但一直没有当一回事,因为煮的饭还是好的。

前不久,听国内的游客去日本旅游时往家带马桶盖,电饭锅。遂有意淘汰美的电饭锅。

网上做了些调查,众说纷纭。有的把日本电饭锅说的神乎其神,有的则认为没有什么差别。

我农民出生,吃过好米,糟米。反正在北大上学时每月9斤米大多跟同学换成面或玉米粉,因为学校供应的米实在比家乡的米差多了。所以始终认为米饭的好坏最大程度上跟米的质量有关,而跟锅不应有太大关系。

买还是不买,有些犹豫。老婆说,电饭锅是家里常用的家电。我心领神会,就买了一个欧洲版Zojirushi NL-AAQ10,模糊逻辑的 (好像IH技术已经过时?)。


MY VERDICT: 没有那么神奇(网上有人说可以空口吃三碗,我认为他是饿的,得罪了)。不过较那个前任,美的电饭锅,这个象牌内釜(内锅)热水清洗时,没有异味。也算物有所值。

Monday, 6 April 2015

忆父亲 (三)

父亲在另一个世界还好吗?

记得有一次梦里见到父亲,我问他,你在干什么?他笑眯眯地说,我在看门。后来跟姐说起此事,姐说你没有问问爹在哪里,哪个单位看门?我说我问了,可父亲笑而不语。

我少不更事的时候是一个无神论者,但父亲去世后,我更愿相信天堂的存在。难道父亲是一个天堂的守门人?

Saturday, 4 April 2015

忆父亲 (二)

今年(2015)的农历清明节,适逢西方的复活节,我因而有暇整理一些文字,以纪念我逝去的父亲。

父亲生前曾在杨园乡(江苏常熟)花木公司工作,有机会去附近省市出差,采购“奇花异石”。有一次出差期间算了命,我已不记得是他主动的,还是“被算命的”,算命先生说将来他“老千年”(过世的意思)的时候,只有三个子女在身边。我兄弟姊妹四人,就我离开故土,孤身一人在北京工作。春节回家时,母亲将这个故事告诉我,并说将来只有我可能不在身边。父亲坐在一边,点上他的烟,微笑不语。

我当时也是一笑了之,因为父亲那时才五十出头,且北京到上海的特快只要17个小时。

可两三年后父亲因胰腺癌离世。在他生命的最后几天,我回到了他的身边。八年后,我离开北京,到英国工作。从此,清明的时候,我再无机会在父亲的骨灰盒前叩首!难道这是算命先生真正所指?

愿父亲在另一个世界能感受到我对他的思念,无论我在天之涯,海之角!

忆父亲 (一)


这是朋友微信里分享的一个LINK,我拿来用了。

远离故乡,无法在清明时节去扫墓,只能静静的坐着,点燃一柱心香,任时光倒转。。

父亲离开我们已经23年了,现在偶尔在梦里能见到他,醒来不再痛苦,而是一种幸福的回忆。

前晚,父亲如约前来,他说要带我见一个成功人士,生意做得蛮大。梦里我心想自己已快50岁的人了,还能有什么发展?但我还是去了。那是一个巨大的饮食城,我去了一趟厕所,出来父亲却不见了。我找啊找,就是找不见。别人建议我打电话,可我的电话本上没有父亲的号码。。。

没有办法,我只能从这一头走到另一头,来回好几次。很幸运,最后我终于找到了他。

他背对着走廊,等我转到他的正面,我看到的父亲是那样的年轻,四十来岁,头发往后梳得必挺。。。

今天,兄弟姐妹一定都去看父亲了。父亲却依然见不到我。心念至此,禁不住泪流满面。

点燃一柱心香,我深感歉意的内心稍许得以慰藉。

Friday, 3 April 2015

Wednesday, 8 October 2014

Build ADFS lab to evaluate the result of claim rule transformation

Sounds like there is not a good utility or log which can tell the claim rule transformation result in ADFS. I followed the instruction in "How to Build Your ADFS Lab on Server 2012, Part2: Web SSO" and built my own lab in which I use DualShield as SAML IDP. Please read the details in this link, and see how to test the result of claim rule transformation in an example "Integrate DualShield with UltiPro"

Integrate DualShield with UltiPro

Ultipro utilizes ADFS2 to accept SAML from IdP, and it requires UPN as one of the issued identities. Please read the details in this link.

Wednesday, 14 May 2014

SAML Authentication on F5 Big-IP (Part 5)

It is time to have a conclusion on this subject.

F5 support team finally lost interest, they didn't reply my question any more, because I was only a trial user I think. I had to put this issue aside for weeks.

Once I thought I had insightful understanding on SAML, especially the XML signature, I decided to review this issue again by myself.

When my eyes rested on the attribute WantAssertionsSigned in F5 BigIP metadata,

I immediately realized I got the answer! IDP sent a SAML response which signed the signature on the whole response, however F5 BigIP appliance specified to expect the signature on assertion part of the response.

After modifying the response (calculate the signature to assertion part), it worked!

I blushed with embarrassment at that time, as SAML authentication on F5 BigIP did work (at least it accepted signature on assertion, not sure it accepts the signature on response). However F5 error message "Digest of SignedInfo mismatch" puzzled everyone.

If we look at the response again, now it is very obvious that the signature was on Response (instead of Assertion, just compare the value of Reference URI with the _IDs)!


Silly me! but could F5 error message become more intuitive?

Friday, 2 May 2014

Password Pass-over In NetScaler

NetScaler supports SAML authentication, and you can pass over the username from IDP to NetScaler through SAML response (see the details in this link). This is very useful when you want to single sign on XenApp, it will pre-fill the username field in CWI login.

Ideally it would be perfect if we could pass over the password as well.

Citrix mentioned the SAML response generated by NetScaler Gateway virtual server could contain password. The vpn SAML profile can have a parameter called "sendpassword". Please see the details in How to Configure SAML SSO Authentication between NetScaler Gateway and Load Balancing Virtual Servers. It implies NetScaler supports the password pass-over, internally at least.

I was very curious if the third-party IDP could take the advantage, so I dug into NetScaler module.

The SAML response generated by NetScaler itself contains password attribute.

<saml2:Attribute Name="password" NameFormat="urn:oasis:names:tc:SAML:2.0:attrname-format:basic"><saml2:AttributeValue xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"  xsi:type="xs:string">the encrypted password</saml2:AttributeValue></saml2:Attribute>

How is the password encrypted? If the third-party IDP follows the rule, it may be able to pass over the password!

The password is actually scrambled by vpn_global_key, which is initialized randomly during system boots up.


ns_sslvpn_copy_passwd(char* srcpass, char* dstpass, unsigned int len)
{
for (int  i = 0; i < len; ++i )
dstpass[i] = srcpass[i] ^ vpn_global_key[i];

}


In ns_aaa_saml_auth, the password (if it exists) is restored.


if ( (unsigned int)(len - 1) <= 0x7E )
{
ns_sslvpn_copy_passwd(src, dst, len);

}

Unfortunately, I don't think there is a way to transmit the vpn_global_key over SAML Request which is the only way the IDP get the information from NetScaler, so my conclusion is, currently it is impossible for the third-party IDP to pass over a valid password value to NetScaler.

Thursday, 1 May 2014

MSI Major Upgrade by Wix

Wix provides an element MajorUpgrade to make a major upgrade a little bit easier, You still need to pay a lot of attention on the sequence and conditions on custom actions, if you have any.

In MSI, upgrade actually contains two parts: uninstall and install. Which one is done first. it is decided by the attribute Schedule. For instance, if Schedule = afterInstallValidate, this scheduling removes the installed product entirely before installing the upgrade product. While Schedule = afterInstallExecute, it installs the upgrade product "on top of" the installed product then lets RemoveExistingProducts uninstall any components that don't also exist in the upgrade product.

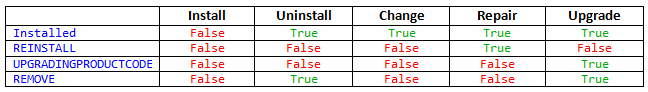
If you have any custom action, for example, retain data file during upgrade, register and start service after installation, stop service and unregister service before uninstallation, inevitably you want to utilize some built-in properties like “Installed”, “UPGRADINGPRODUCTCODE”, “REMOVE”,“REINSTALL”. On StackOverflow, there is a good summary which I copied it here.


As I pointed out earlier, an upgrade consists of two phases, you may wonder, are these property values are same in two phases? Unfortunately, the listed values under “Upgrade” actually apply to the uninstall phase of upgrade. The install phase of upgrade has same values on this properties as a new install, which means you can’t tell the difference with these properties between a new install and the install part of upgrade. I would suggest you writing a vbscript type custom action to check something else directly.

Assume you have installed a product with version1.msi, now you are going to upgrade it with version2.msi. Remember, the install part of upgrade will use version2.msi, but the uninstall part of upgrade will use version1.msi which was saved somewhere when you first installed it.


Saturday, 22 March 2014

Lync Lab in ESXi

Recently I set up an on-premises Lync server lab with ESXi. Something learned from the experiment are.

  • Before installation, carefully read Microsoft Lync Server 2013 Protocol Workloads Poster. Apart from the network diagram, also try to fully understand the DNS Configuration and Certificate Requirements.
  • SIP domain can be different from AD domain. In my example, AD domain = nanoart.local, but SIP domain = nanoart.co.uk.
  • The server certificate for Lync Edge server external NIC must have CRL Distribution Points . If using my OpenSSL shell script in previous blog, enable the line,
crlDistributionPoints = URI:https://$CN/crlempty.crl

You need a physical machine as ESXi host, install 5 VMs. 1: Domain Controller, 2: Lync 2013 Standard Server Edition, 3: Lync 2013 Edge server, 4: TMG 2010, 5: DNS server.

Apart from it, you also need a desktop test machine, one wireless AP and a mobile phone.

Here is my lab's network diagram.


This is the external DNS configuration.


Read more at ....

Cisco ACS 5.4 in ESXi

There are some tutorials on Internet which teach you how to apply the cracked licenses onto ACS 5.2. I found they are still valid for ACS 5.4. The procedure is quite same apart from that you need to remove GRUB password protection in ACS 5.4.

Read more at the link.

Wednesday, 12 March 2014

OpenSSL to generate certificate in single shell script

Are you looking for a Linux shell script which can generate a certificate? Ideally, you only need to give a parameter, for web site certificate, which is its FQDN. You don't care other information, and you are fed up with the interaction which asks you input Country, Organization etc. In that case, here it is.

I use certificates quite a lot. Recently I was asked to set up Microsoft Lync server(s). The certificates on Lync Reverse Proxy and Lync Edge server must have SANs (subject alternative name). It drove me to write such a shell script.

You are encouraged to change the configuration part in the shell script, for instance, key length (2048 by default), key password (PFX password, = "changeit"), how long the generated certificate will be valid(10 years)?

You can run this script without any parameter to see its usage

# ./certgen.sh
Usage:
  certgen ca
  certgen client
  certgen server []


First of all, you need to create CA certificate. Just run "certgen ca", it will create two files, cacert.crt and cakey.pem. Back up these two files, you are going to use this CA to sign the server/client certificates afterwards.

Now you can generate a server certificate, for instance, run the following command,

./certgen.sh server fruit.myorchard.local DNS:apple.myorchard.local,DNS:cherry.myorchard.local

You are expected to see the result

Generating ca_config.cnf
generating server cert for:fruit.myorchard.local
Generating a 2048 bit RSA private key
.........................................................+++
.....................................................................................................................................................................................................................+++
writing new private key to 'fruit.myorchard.local.key'
-----
Using configuration from ca_config.cnf
Check that the request matches the signature
Signature ok
Certificate Details:
        Serial Number: 4 (0x4)
        Validity
            Not Before: Mar 12 11:44:40 2014 GMT
            Not After : Mar  9 11:44:40 2024 GMT
        Subject:
            countryName               = GB
            stateOrProvinceName       = BUCKS
            localityName              = LONDON
            organizationName          = YOURCOMPANY.COM
            organizationalUnitName    = R&D
            commonName                = fruit.myorchard.local
            emailAddress              = support@yourcompany.com
        X509v3 extensions:
            X509v3 Extended Key Usage:
                TLS Web Server Authentication
            X509v3 Key Usage:
                Digital Signature, Key Encipherment, Data Encipherment
            X509v3 Subject Alternative Name:
                DNS:fruit.myorchard.local, DNS:apple.myorchard.local, DNS:cherry.myorchard.local
Certificate is to be certified until Mar  9 11:44:40 2024 GMT (3650 days)

Write out database with 1 new entries
Data Base Updated
Generated files: key: fruit.myorchard.local.key , cert: fruit.myorchard.local.crt

If you see "failed to update database TXT_DB error number 2", it is very likely you have already generated the certificate with the same FQDN. You need to edit the index.txt file to remove the related entry.

See more at this link.

Reference


Generating Self-Signed Test Certificates Using One Single Shell Script 

Friday, 10 January 2014

Encode/Decode Citrix Password in NFuseProtocol

In Citrix NFuseProtocol, password is encoded, not the one you typed. If you capture the traffic between Citrix  Receiver and PNAgent (Now it is called XenApp Service) web site, you will see the typical post data.

<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE NFuseProtocol SYSTEM "NFuse.dtd"><NFuseProtocol version="4.6">
    <RequestReconnectSessionData>
        <Credentials>
            <UserName>administrator</UserName>
            <Password encoding="ctx1">NFHALEBBMHGCLEBBMDGGKMAJNOHLLKBP</Password>
            <Domain type="NT">CONTOSO</Domain>
        </Credentials>
        <ClientName>REMLAPTOP</ClientName>
        <ClientName>REMLAPTOP</ClientName>
        <ServerType>win32</ServerType>
        <ClientType>ica30</ClientType>
        <SessionType>disconnected</SessionType>
        <SessionType>active</SessionType>
    </RequestReconnectSessionData>
</NFuseProtocol>


Ever wonder what is the original password of the encoded one "NFHALEBBMHGCLEBBMDGGKMAJNOHLLKBP"?

Here is the tool you can try.

For encode, do

citrixpassword.exe encode "password"

It will output the result

hash password = NFHALEBBMHGCLEBBMDGGKMAJNOHLLKBP .

For decode, do

citrixpassword.exe decode NFHALEBBMHGCLEBBMDGGKMAJNOHLLKBP

The result will be,

original password = password .

Don't ask me to publish the source code, I think it is not wise to do that. However the algorithm is very simple, just some XOR operations. You can work it out easily by disassembling my tool.


Reference

Encoding and Decoding Citrix Passwords

Mac OSX Authorization Rights and Rules.

Before Mavericks (OSX 10.9),  right and rule are separated in authorization database, which is the file /etc/authorization.

The API AuthorizationRightGet/Set/Remove can only operate on rights. If you want to manipulate the rules, you have to modify the file  /etc/authorization  directly.

On Mavericks, the file is deprecated.  Apple’s engineers have chosen to mix rights and rules in this single table. Now the API can operate on the rule as well as on the right. The security binary (the command security authorizationdb read/write ) also succeeds on read/write rules.

It is an improvement, although now I can't easily tell which is right, which is rule.

Read more...

References

Authbuddy

Authorization Rights and Mavericks

Modifying the OS X Mavericks Authorization Database

Saturday, 14 December 2013

Install ESXi on MB GA-H87-HD3

ESXi 5.5 can be run on the motherboard Gigabyte GA-H87-HD3 Socket 1150 VGA DVI HDMI ATX Motherboard.

This is component list


  • Gigabyte GA-H87-HD3 Socket 1150 VGA DVI HDMI ATX Motherboard
  • Toshiba 2 x 3TB Internal Hard Drive 
  • Crucial 4 x 8GB DDR3 1600MHz Ballistix Sport Memory
  • Intel Core i5 4670 3.40GHz Socket 1150 6MB Cache Retail Boxed Processor
  • Coolermaster Elite 330 Case With Coolermaster eXtreme Power 500W PSU


Read more...